The Center for Security Studies at ETH Zurich recorded 407 cyber operations against space-related organizations in 2025, an average of more than one a day across the year. The count comes from a new threat landscape report by senior cyberdefense researcher Clemence Poirier, who has tracked cyber activity against the space sector at the Zurich-based think tank since 2022.
A roster dominated by hacktivists
The 407 incidents affected at least 183 distinct space-related organizations, spanning commercial operators, government agencies, and research institutions, and involved 139 identifiable threat actors, according to Industrial Cyber's summary of the findings. Hacktivist groups made up most of that roster, a shift from earlier years when state-linked groups drew more of the research attention. Poirier told Industrial Cyber that ransomware, data leaks, and credential theft also hit the sector throughout the year, with activity correlating closely to major geopolitical crises.
DDoS, ransomware, and the ground segment
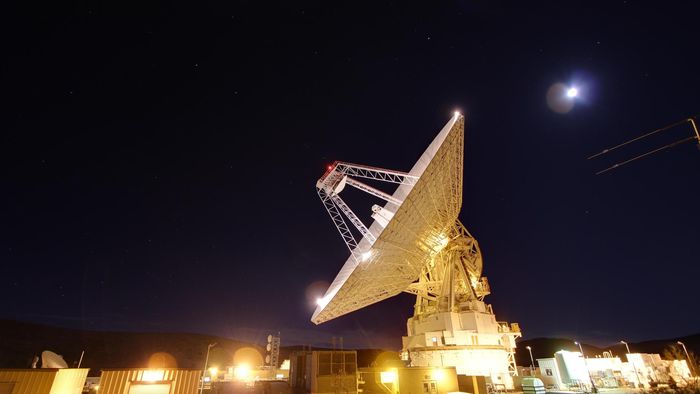
Distributed denial of service made up 61 percent of the 407 operations, Via Satellite reported, with ransomware accounting for 13 percent and data breaches for 5 percent. None of the activity reached a satellite in orbit. Every incident in the report struck terrestrial infrastructure instead: ground stations, corporate networks at space companies, and user modems on customer premises.
Why a clean orbital record is not reassuring
Poirier addressed that gap directly in a companion piece for the World Economic Forum, arguing that the absence of documented attacks on orbiting spacecraft does not establish that they are unaffected. Most satellites still carry no onboard capability to detect malicious cyber activity, so an intrusion in orbit could go unnoticed long after the fact. The visible record, in other words, measures what ground-based monitoring tools happen to catch, not what the full threat surface actually looks like.
A defense contractor caught by Interlock
One incident folded into the 2025 count illustrates the trend. In May 2025, the ransomware group Interlock claimed to have exfiltrated roughly 4.2 terabytes of data, nearly 3 million files, from National Defense Corporation and its subsidiary AMTEC, a maker of ammunition handling systems owned by National Presto Industries, according to Kratos Space's account of the breach. The leaked files reportedly referenced customers across the defense and space supply chain. Analysts quoted in that reporting noted that Interlock had shown little prior interest in space-adjacent targets, and some suspected the operation carried state backing, though no attribution has been confirmed.
Tracking conflict in the incident log
CSS research published in November 2025, covering January 2023 through July 2025, found a similar pattern tied to real-world fighting. That earlier report logged 237 cyber operations against the space sector over the period, with a single-month spike of 72 operations in June 2025 that coincided with the Israel-Iran escalation. The 2025 full-year count suggests that pattern held: cyber activity against the sector tracks geopolitical flashpoints closely enough that researchers can often tell which conflict drove a given spike.
Space ISAC, the information-sharing body that aggregates threat intelligence for the sector, added two new members during the reporting period: Resecurity on August 4, 2026, and the European firm DamoTech a week later, on August 11.
First reported by the Center for Security Studies at ETH Zurich, with coverage from Via Satellite and the World Economic Forum.