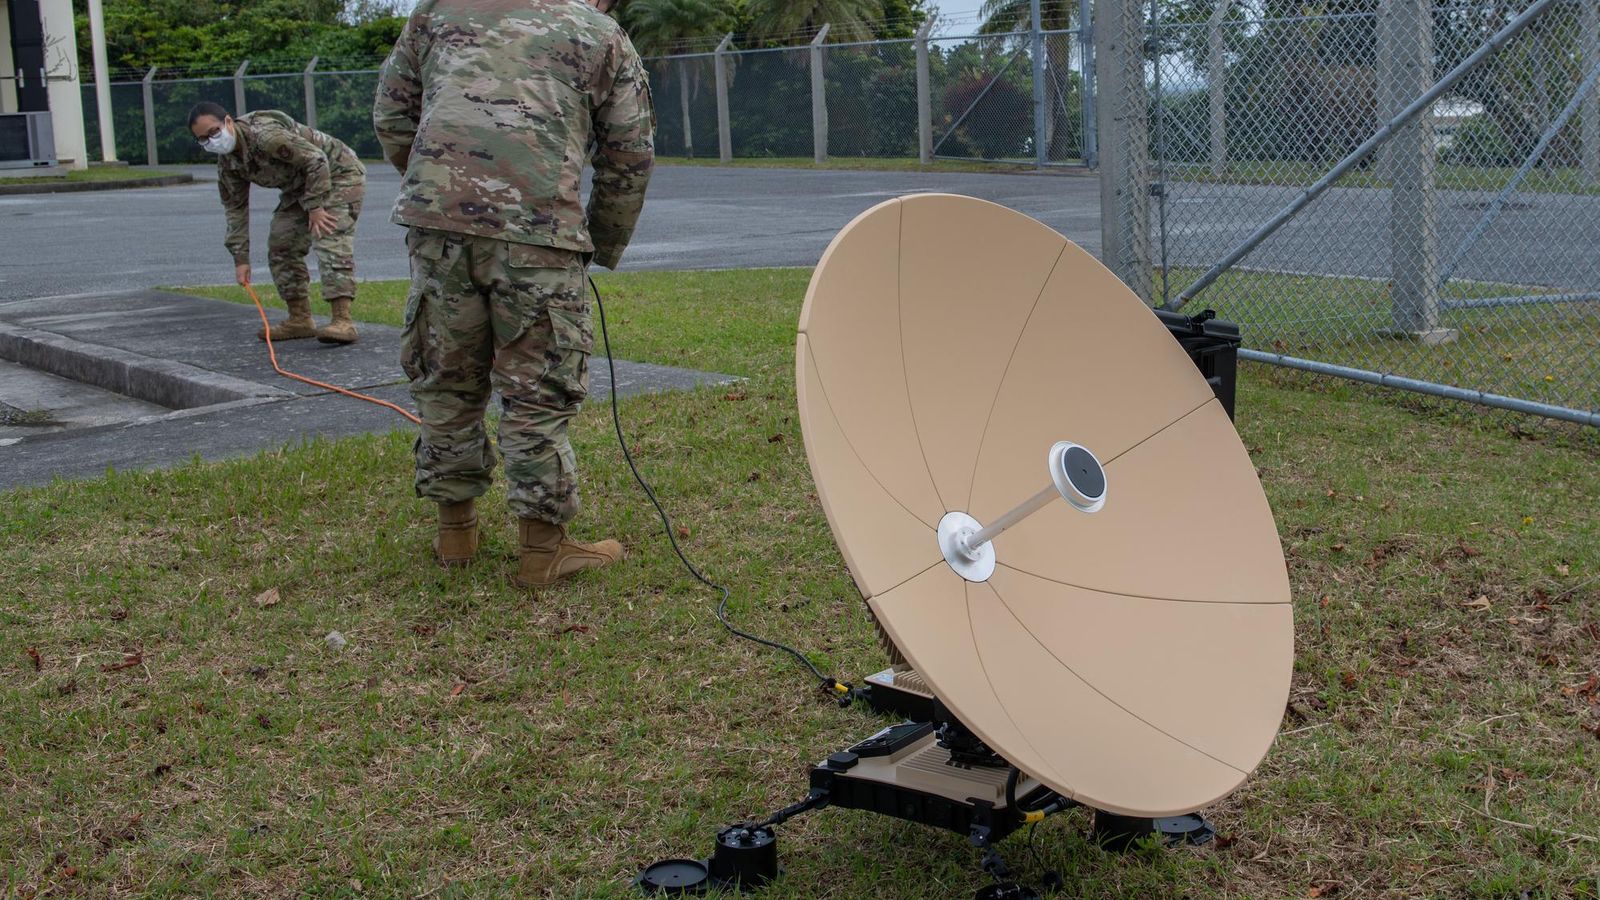
On September 2, 2026, Darknavy, a cybersecurity research institute based in Singapore and Shanghai, posted on social media that it had achieved full administrative root access to SpaceX's newest Starlink user terminal, the square-antenna "Standard Actuated" model. The South China Morning Post reported that the group used what it called "sophisticated hardware attacks" to run arbitrary code on the device, but withheld its exact method, saying details would appear later on its own site. The claim requires physical access to the dish, so it is a lab exploit rather than a remote, mass-scale hack. It is still the second time in four years that a hardware attack has reportedly broken into a Starlink terminal SpaceX had already hardened.
A Pattern That Started in 2022
In August 2022, KU Leuven researcher Lennert Wouters presented the first public break of the Starlink terminal at Black Hat USA in Las Vegas. His attack used a voltage fault injection rig built around roughly 25 dollars of parts: a Raspberry Pi microcontroller, flash storage, electronic switches and a voltage regulator, soldered onto the circular first-generation dish. The glitch struck during the system-on-chip's ROM bootloader, bypassing firmware signature verification and opening the door to unsigned code. Wouters disclosed the flaw through SpaceX's bug bounty program before going public, and the company's written response called the work "technically impressive." SpaceX then disabled the terminal's UART debug interface in a firmware update, closing the specific path Wouters had used.
Software Flaws Followed the Hardware Ones
Hardware was never the only attack surface. In March 2023, a University of Oxford team, Joshua Smailes, Edd Salkield, Sebastian Köhler, Simon Birnbach and Ivan Martinovic, published "Dishing Out DoS: How to Disable and Secure the Starlink User Terminal", describing a fuzzing campaign against the dish's administrative interface. A single crafted command froze the terminal's command handler: the dish kept receiving and modulating signal but stopped responding to new instructions until someone power-cycled it. The team warned that repeated misuse could also drive the dish's steering motors past their design limits, and that under some conditions the crash might be triggered without a long-term presence on the local network.
A newer software flaw surfaced on August 15, 2026, when CVE-2026-19918 was published against the Starlink Router Gen 3 running firmware 2025.11.14.mr64708.3. The bug sits in the get_status function of the same gRPC management interface the Oxford team had fuzzed three years earlier: an access control gap lets any device already on the terminal's local network read status data, including dish orientation and connected-device details, without authenticating first. Trackers rate it medium severity, with CVSS scores ranging from 5.3 to 6.3 depending on the scoring version, and list no response from SpaceX to the initial disclosure and no published patch.
Why a Ground Box Keeps Drawing Attention
None of these four disclosures reached the satellites themselves. Each one targeted the box bolted to a wall or staked into the ground, the point where a home network, a ship's bridge or a forward operating base meets the constellation overhead. CISA and the FBI flagged that same ground segment back in 2022, warning satellite communications providers and customers to strengthen access controls and monitor for unusual activity. A compromised terminal can be repointed away from the sky, taken offline at a chosen moment, or used as a foothold into whatever network it serves, from a home router to a vessel's onboard systems.
SpaceX's May 2026 prospectus for its planned Nasdaq listing put Starlink's active subscriber base at 10.3 million across 164 countries and territories as of March 31, 2026, served by a constellation of roughly 9,600 satellites in low Earth orbit. Each household router and field terminal in that count runs some version of the firmware Wouters, the Oxford team, VulDB's tracked disclosure and now Darknavy have each taken a turn trying to break.
Darknavy's claim was first reported by the South China Morning Post.